
NEW FEATURE - SECURITY DEVICES & AGENTS
Higher tier networks are actively monitored. Defended LANs include a dedicated
monitoring appliance, a Splunk SIEM, a Cisco Firepower IPS, or a Suricata IDS.
Every monitored box runs one security agent matching to the appliance
- Splunk's splunkd forwarder port 9997
- Cisco Secure Endpoint's ampdaemon, port 443
- Elastic's filebeat port 5044
- Gateways and FreeBSD boxes have syslog-ng on port 514
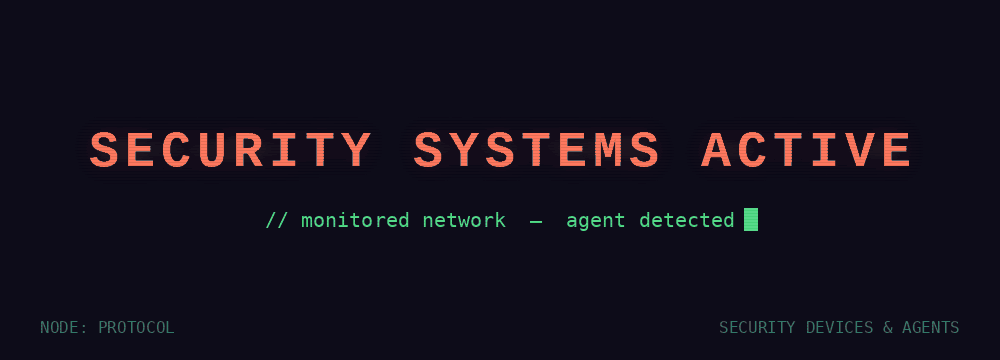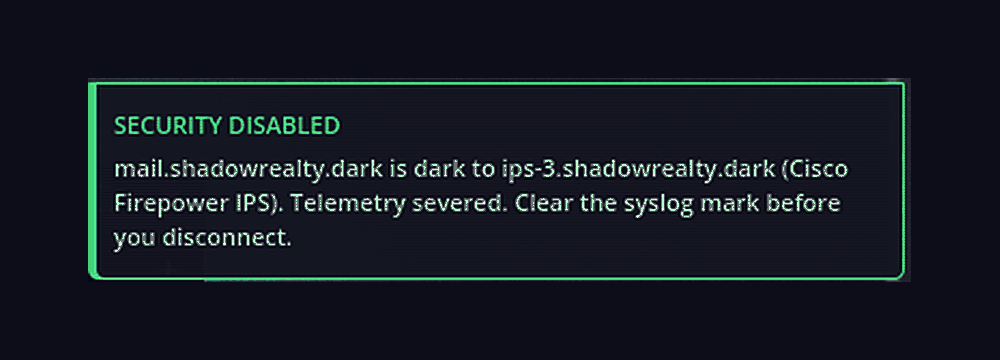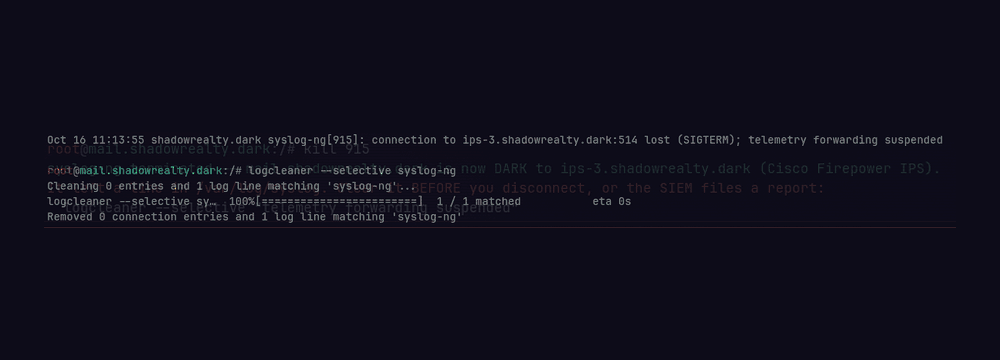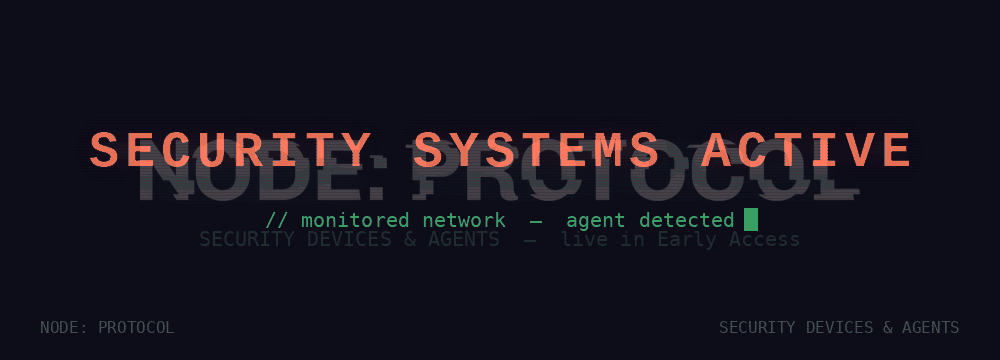
While the agent is running it makes you easier to get traced on that box. You can spot it in the known commands ps, ss, netstat and lsof, read its config off disk, once you have root, take it offline with kill, systemctl stop, or service stop on FreeBSD. Going dark raises your heat and drops a line in the box's syslog, disconnect with that line still there and the target reports a strike against you.
Remove that first with "logcleaner --selective" for the clean get away.
To make sure players are familiar with this new feature, six contract types are now offering the optional agent-kill bonus when the target sits on a monitored network. Take its security agent offline and remove the syslog line for extra BTC, always optional, but never required to finish the mission.
[+] Server takedown - knock their infrastructure offline so it reads as a
fault, not an attack
[+] Surveillance blackout - blind the camera grid and the SIEM that watches it
[+] Data theft - pull the file before the transfer ever reaches their console
[+] Data destruction - erase the records so the wipe reads as data loss, not sabotage
[+] Record tampering - alter the entry with nothing logging that it changed
[+] Data poisoning - corrupt the source so it looks like drift, not tampering
NEW
[+] Pegasus operator console: a new feature that can infect android and iphones based on patch level.
The dashboard can be reached from the new PEGASUS tab in DarkMarket.
This feature is still under active development. So for beta testers, I would love feedback!

[+] Native gateway consoles: Cisco gateways now drop you directly into the IOS CLI,
pfSense firewalls into the numbered console menu, and Citrix NetScaler into the nscli shell. Underlying shell still available
[+] SIGINT EXPLOIT REFERENCE: the Operator Handbook now carries a full, searchable reference for every phone and radio exploit
REALISM & SYSTEMS
[+] systemctl (Linux) and service (FreeBSD) are now real. stopping a service
takes it offline. It drops from ps/top/lsof and its listening port closes in ss/netstat/sockstat
[+] kill now stops a daemon either by PID or pidfile
[+] Linux server recon is now consistent, advertised ports are backed
by a real daemon in the process list
[+] Linux Domain Controllers present as Samba/Heimdal boxes
[+] Cacti monitoring boxes answer SNMP, this can be used for recon
[+] Each database box now has one realistic admin password, consistent
with the configs and for use with sqlmap
[+] Cracked credentials and hydra web brute-forces now carry into the LAN's web
admin panels
[+] Windows RDP credentials reuse across the network
[+] Stealth miners live roughly 12 real hours, and dead or detected miners are
removed from the list automatically
[+] Postal ops shipping addresses must match the target's whois registration
TRACE, HEAT & STEALTH
[+] Heat driven auto-investigations no longer skips past an active proxychain.
[+] analyze --live runs until the trace clears, not for two-minutes.
[+] Phones and FreeBSD boxes now include a baseline /var/log/syslog, so a surgical
log clean can no longer look like tampered
[+] proxychains --tor flag gives real feedback, and the nmap stealth override warning now
names the actual flags
CO-OP & RIVALS
[+] MeshLink saves your crew name, handle and clan tag between sessions
[+] A Fed Raid in co-op now shows the raid screen to the operator who was
caught, and keeps MeshLink open for the other crew members
[+] IDS scan-detection intel is now only scoped to the active operation
[+] The Wire page now offers a rival elimination briefing to your inbox
[+] Cobalt Strike C2 pivots now use domain credential reuse, and a seized C2
recovers its detection
INTERFACE & QUALITY OF LIFE
[+] The Operator Handbook is now fully copy-pastable: click any command to copy
it, also search highlights are added
[+] New desktop wallpaper set! Based on the new art
[+] Vigilance now shows a popup message with a heads-up if the target opens an investigation
on you. This gives you a better overview without monitoring meshmail
[+] LeakedDB now also shows the breached phone number for use with Pegasus
[+] FaceLink Back button returns to your search results, also DM social
engineering no longer has the trust bug
[+] Botnet overview labels the count infected machines
UPCOMING
Steam next fest is around the corner, only three days to left, If you have not yet tried the demo, you are missing out! See you on Monday the 19th with livestreams and an puzzle to solve. You can win 5 BTC in game currency for the early access release.